Automated bot swarms scan millions of public IP addresses daily. They don’t compromise infrastructure with complex exploits; they systematically target exposed administrative endpoints, missing HTTP security headers, and outdated dependency packages.
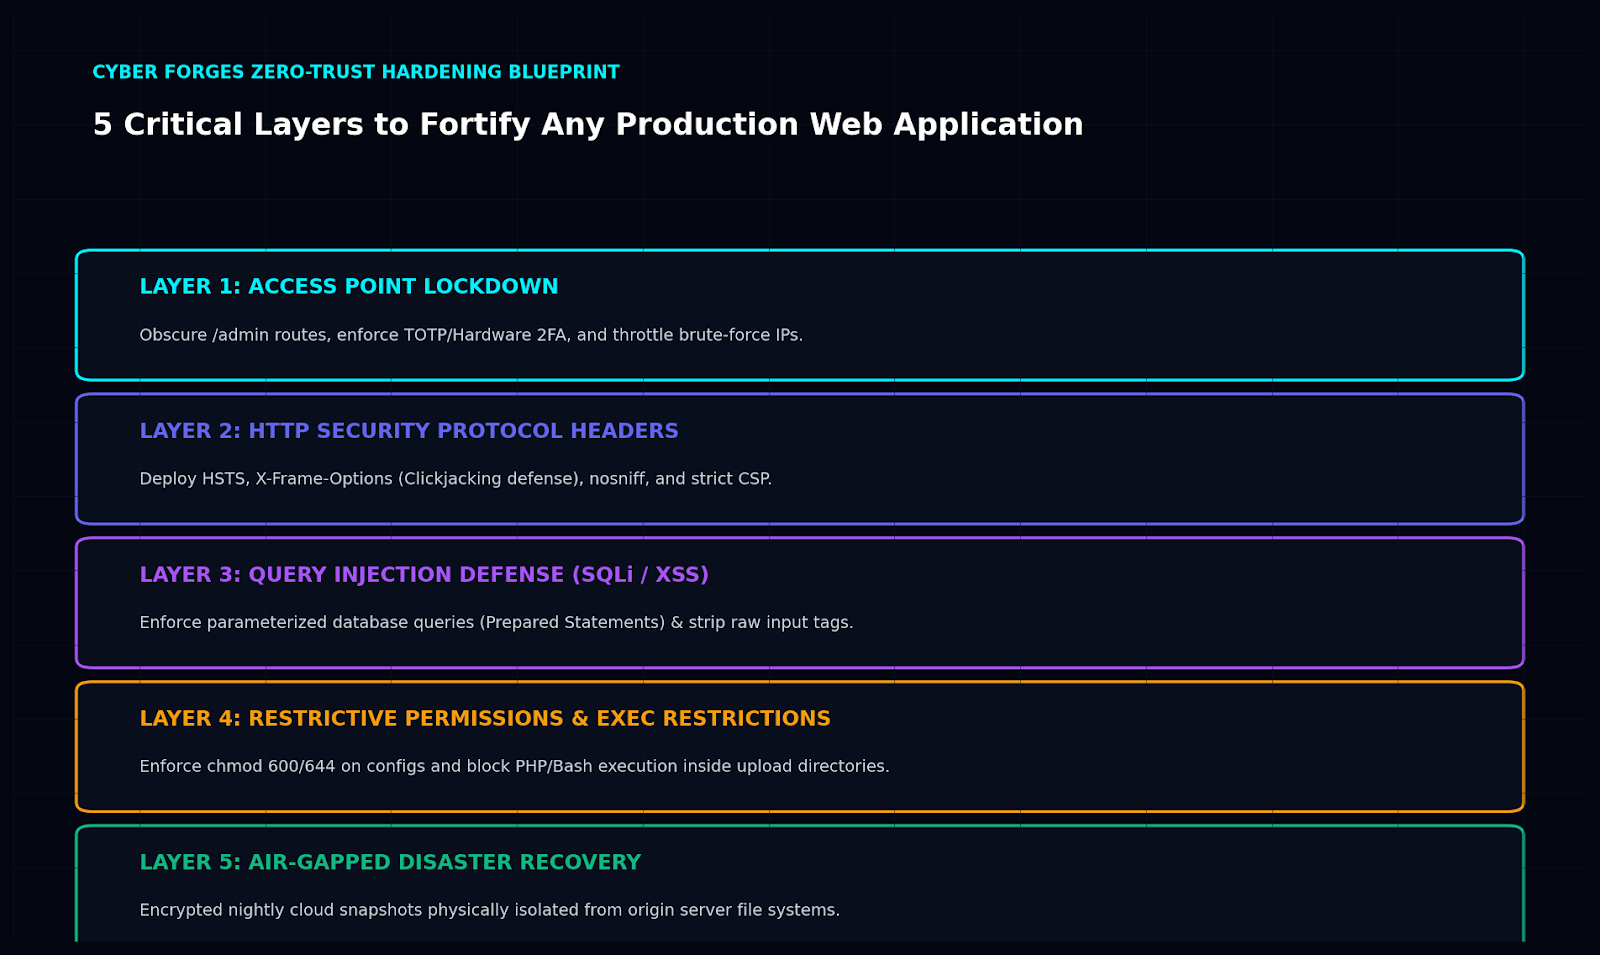
01 Admin Perimeter & Brute-Force Neutralization
Never expose /admin or /wp-login.php to public scrapers. Relocate your gateway to an obfuscated route and enforce strict rate-limiting.
Passwords leak via phishing and credential stuffing. Time-based token auth blocks unauthorized sessions even when passwords are breached.
02 Production HTTP Security Directives
Modern browsers provide sandboxing engines that only activate when instructed by HTTP response directives:
03 Air-Gapped Snapshot Recovery
If backups reside on the same server volume, an attacker who gains root access deletes both your site and your recovery images simultaneously. Cyber Forges enforces daily air-gapped snapshots pushed off-site, making data loss mathematically impossible.
Is Your Platform Exposed to Vulnerabilities?
Deploy enterprise-grade WAF rules, hardened container isolation, and continuous vulnerability audits. Speak directly with Cyber Forges security engineers.
⚡ Request Deep Security Audit